Strategic leadership.
Without the overhead.
Strategic Leadership
Board-level security direction without the full-time executive cost.
Board-level security direction without the full-time executive cost.
Service Overview
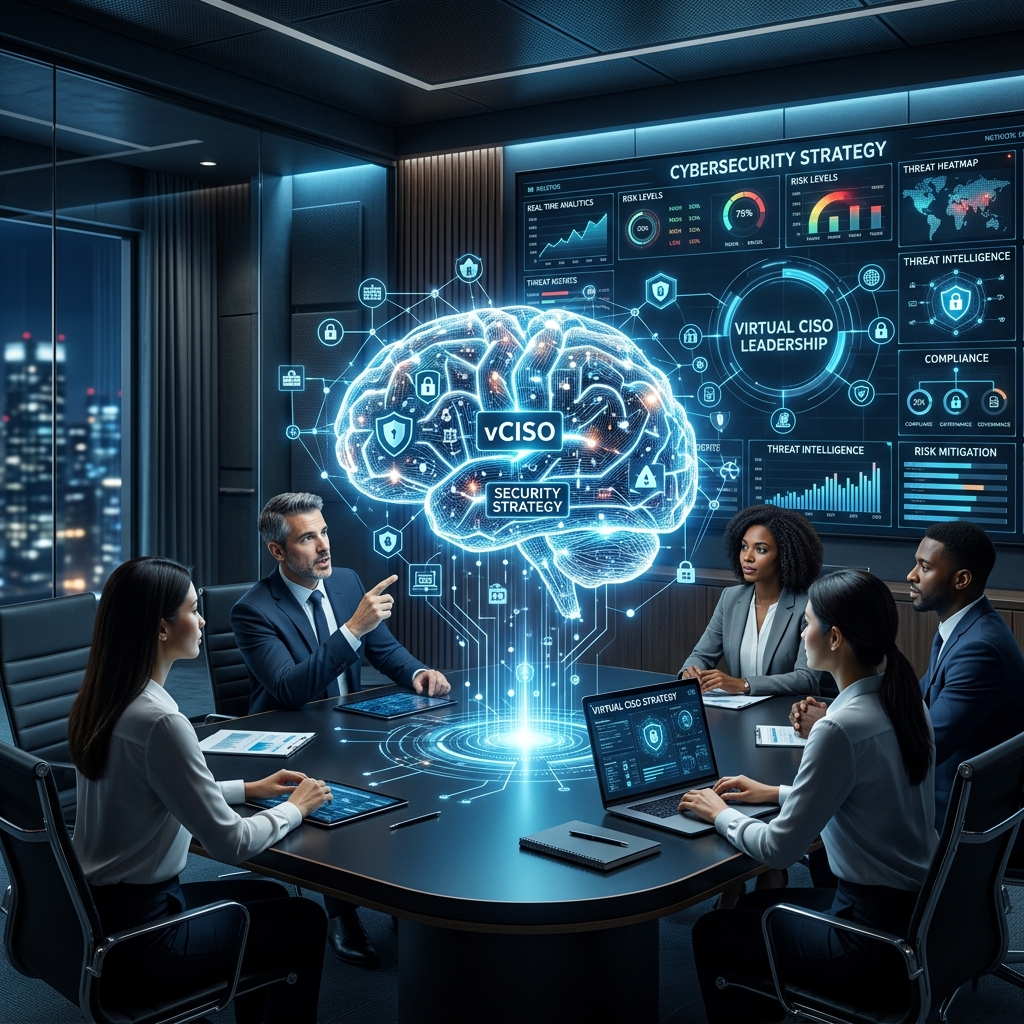
Every organisation needs strategic security leadership - but not every organisation needs, or can justify, a full-time CISO. Our vCISO service provides direct access to a senior security executive who understands your business, represents your security interests at board level, and drives your security programme forward - on a retainer that scales with your needs.
Every engagement is led by a named senior consultant with direct, hands-on experience in this domain. You will always know who is accountable for your work - and have direct access to them throughout.
Discuss Your RequirementsKey Deliverables
Why It Matters
A senior practitioner who can present credibly to your board, audit committee, and regulators - translating complex risk into clear governance language.
Strategic ownership of your security programme - setting direction, managing vendors, and ensuring your security investments are coordinated and effective.
Senior security leadership at a fraction of the cost of a full-time CISO hire - with the flexibility to scale engagement as your organisation grows.
A practitioner who understands your regulatory environment and can represent your security posture to auditors, regulators, and insurers.
Is It Right For You?
A virtual CISO is effective for organisations that want proper security controls in place but cannot yet justify a full-time CISO hire.
If you are a small or medium-sized business looking to put the necessary security controls in place, engaging a virtual CISO is a strong way to start.
Best suited to organisations that:
Our Capability
A complete view of the domains a Rutters vCISO can own on your behalf, scaled to your organisation's needs.
Certification
Data Security
Supply Chain Security
Governance & Compliance
Risk Assessment & Management
Asset Management
Incident Response & Crisis Management
Cyber Resilience & Strategy
Technology Stack
Operational Security
Audits & Assessments
Business Continuity & Disaster Recovery
Cloud Security
Cyber Risk Advisory
Cyber Strategy
Technology Partners
We work across a curated ecosystem of leading GRC, risk, and security management platforms.



How We Work
A structured, proven approach built on years of practitioner experience - transparent at every stage.
Phase 01
Understand your organisation, existing security posture, regulatory context, and board-level risk appetite to define the vCISO mandate.
Phase 02
Establish a clear security programme baseline - priorities, roadmap, budget alignment, and stakeholder mapping.
Phase 03
Regular executive engagement, board reporting, vendor oversight, incident management, and programme governance on an agreed retainer basis.
Phase 04
Formal quarterly reviews to assess programme progress, adjust priorities, and report against agreed KPIs and risk reduction targets.
Why Rutters
Every vCISO engagement we deliver is led by a practitioner with direct, hands-on experience in this domain. We apply rigorous methodology and communicate findings in a way that drives real action - from technical teams to board level.
Request a ProposalDelivered by practitioners with years of specialist experience, not delegated to junior staff.
No product affiliations. Our recommendations are based entirely on your risk profile and objectives.
Deliverables calibrated to technical teams and executives alike - actionable, not just comprehensive.
We remain available after delivery to support remediation and answer questions as your team acts.
Ready to Start?
Every engagement begins with a confidential, no-obligation conversation. We will respond within one business day and confirm the right next step.
All enquiries are treated in strict confidence.