Structure your defences.
Built to resist.
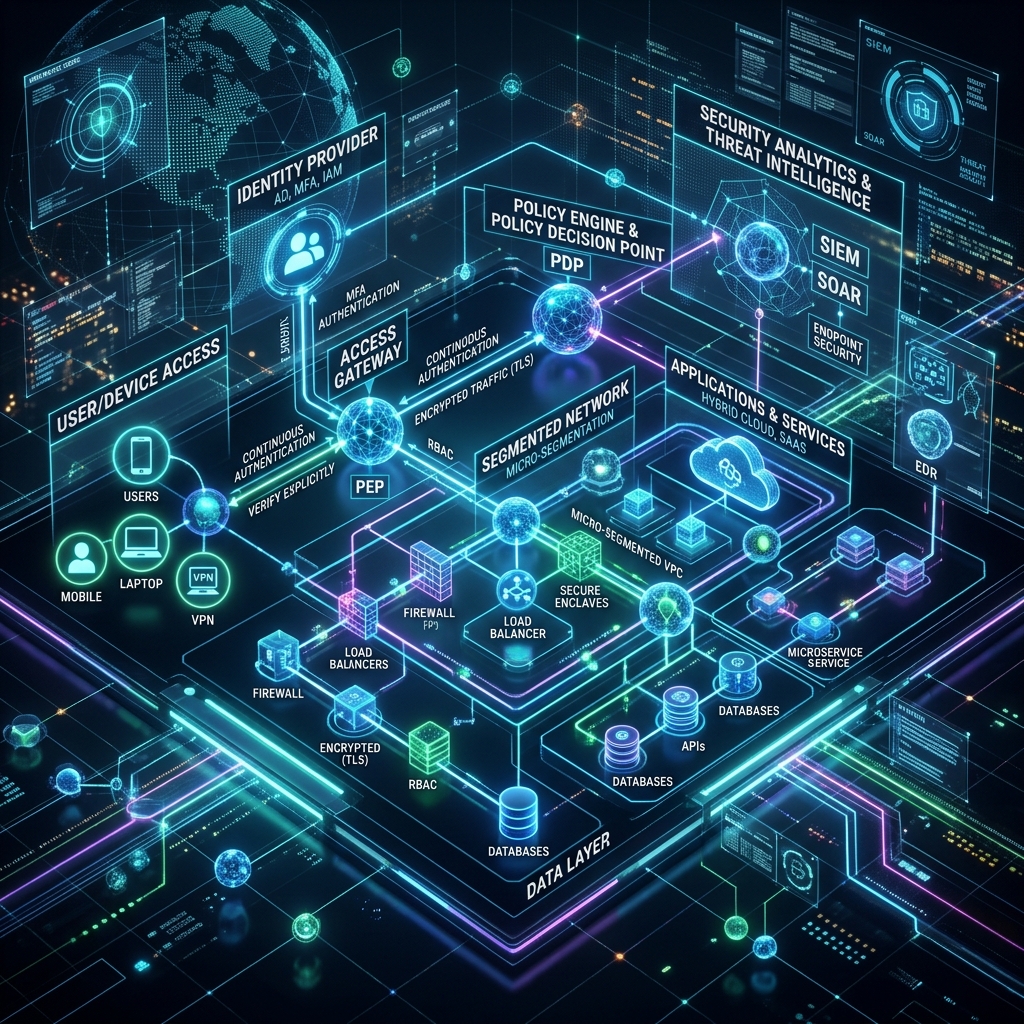
Zero-Trust Design
Build an enterprise architecture designed to resist persistent threats.
Build an enterprise architecture designed to resist persistent threats.
Service Overview
Most organisations have accumulated security controls over time - reactive, overlapping, and rarely designed as a coherent whole. Rutters brings architectural rigour to your security estate. We design security architectures that are coherent, proportionate, and built around the principle of assumed breach - from identity and access management to network segmentation, cloud controls, and endpoint protection.
Every engagement is led by a named senior consultant with direct, hands-on experience in this domain. You will always know who is accountable for your work - and have direct access to them throughout.
Discuss Your RequirementsKey Deliverables
Why It Matters
Architecture designed around identity verification, least-privilege access, and continuous validation - eliminating implicit trust from your environment.
Structured segmentation, access controls, and data flow design that systematically reduces the paths available to an attacker.
Security architectures designed for cloud-native, hybrid, and multi-cloud environments - with controls that follow workloads, not perimeters.
Architecture reviews that identify duplication, gaps, and misalignment - ensuring every security investment adds genuine value.
Our Philosophy
Designing a security architecture is like designing a building - it must be planned before it's built, and every decision must serve the whole.
Complex systems demand a complete understanding of requirements, design philosophy, interoperability, and how components integrate and operate together - never a checklist exercise.
Architecture must securely enable your strategic direction - in current and new markets, channels, and products - grounded in where the business is today and where it's going.
Controls are matched to the realistic risks your organisation actually faces - never applied generically, and never for risks you don't inherently carry.
What It Delivers
Far beyond technical controls - architecture that integrates with how your business plans, governs, and operates.
Business & Strategy
Governance & Risk
Operational Excellence
Our Framework
Every architecture we design starts from an industry-agnostic, standards-based reference framework.
Grounded in TOGAF and SABSA, and influenced by the Cloud Security Alliance's Trusted Cloud Initiative and NIST - the foundation for any enterprise architecture.
Follows the SABSA lifecycle, overlaying the familiar Plan-Do-Check-Act cycle across current, target, and transition states.
Ensures mutual inclusivity between IT and cybersecurity - integrating SOC, NOC, and Fusion Centre concepts, whether in-house or via managed providers.
A comprehensive doctrine applied from design through to the running lifecycle - extendable to account for MITRE ATT&CK and D3FEND.
Built on a core of NIST 800-53, adaptable to ISO 27001, CIS CSC, or CSA-CCM - aligning security mechanisms with regulatory compliance.
Change is constant. Through disciplined, organised design, our architecture practice controls what can be controlled and minimises the impact of what cannot.
Technology Partners
We work across a curated ecosystem of leading security architecture and platform vendors.



How We Work
A structured, proven approach built on years of practitioner experience - transparent at every stage.
Phase 01
Assess your current security architecture against your threat model, regulatory requirements, and zero-trust principles.
Phase 02
Identify and prioritise the threats most relevant to your organisation and design controls proportionate to each risk.
Phase 03
Produce a target-state security architecture with reference designs, control specifications, and migration guidance.
Phase 04
Ongoing architecture assurance - reviewing changes, new projects, and technology decisions against the agreed security architecture.
Why Rutters
Every Security Architecture engagement we deliver is led by a practitioner with direct, hands-on experience in this domain. We apply rigorous methodology and communicate findings in a way that drives real action - from technical teams to board level.
Request a ProposalDelivered by practitioners with years of specialist experience, not delegated to junior staff.
No product affiliations. Our recommendations are based entirely on your risk profile and objectives.
Deliverables calibrated to technical teams and executives alike - actionable, not just comprehensive.
We remain available after delivery to support remediation and answer questions as your team acts.
Ready to Start?
Every engagement begins with a confidential, no-obligation conversation. We will respond within one business day and confirm the right next step.
All enquiries are treated in strict confidence.